GDPR non-compliance carries genuinely severe financial consequences, fines up to 4% of global annual revenue or 20 million euros, whichever is greater, making a chat platform's actual, verifiable compliance posture a genuinely important evaluation factor, not a minor checkbox.
Quick answer: For businesses needing genuine GDPR compliance, Zendesk stands out for offering EU data residency and a comprehensive Data Processing Agreement, while Landbot specifically hosts data in Belgium on EU-based Google Cloud infrastructure, though genuine compliance always depends on verifying a vendor's actual DPA terms, data location, and support for data subject rights rather than a general compliance claim alone.
A vendor's general "GDPR compliant" marketing claim alone doesn't reveal the specific, meaningful details, whether they'll sign a proper Data Processing Agreement, where they actually store data, and whether they genuinely support data subject rights like access and erasure.
Understanding what to verify directly, rather than accepting a general compliance claim at face value, helps a business genuinely protect itself when choosing a chat platform for EU-facing operations.
This guide covers what genuine GDPR compliance requires, platforms known for strong compliance posture, common evaluation mistakes, key questions to ask, and how ChatDrill approaches GDPR-conscious design. This is general information, not legal advice, and compliance should be confirmed with your own legal counsel.
What Genuine GDPR Compliance Requires
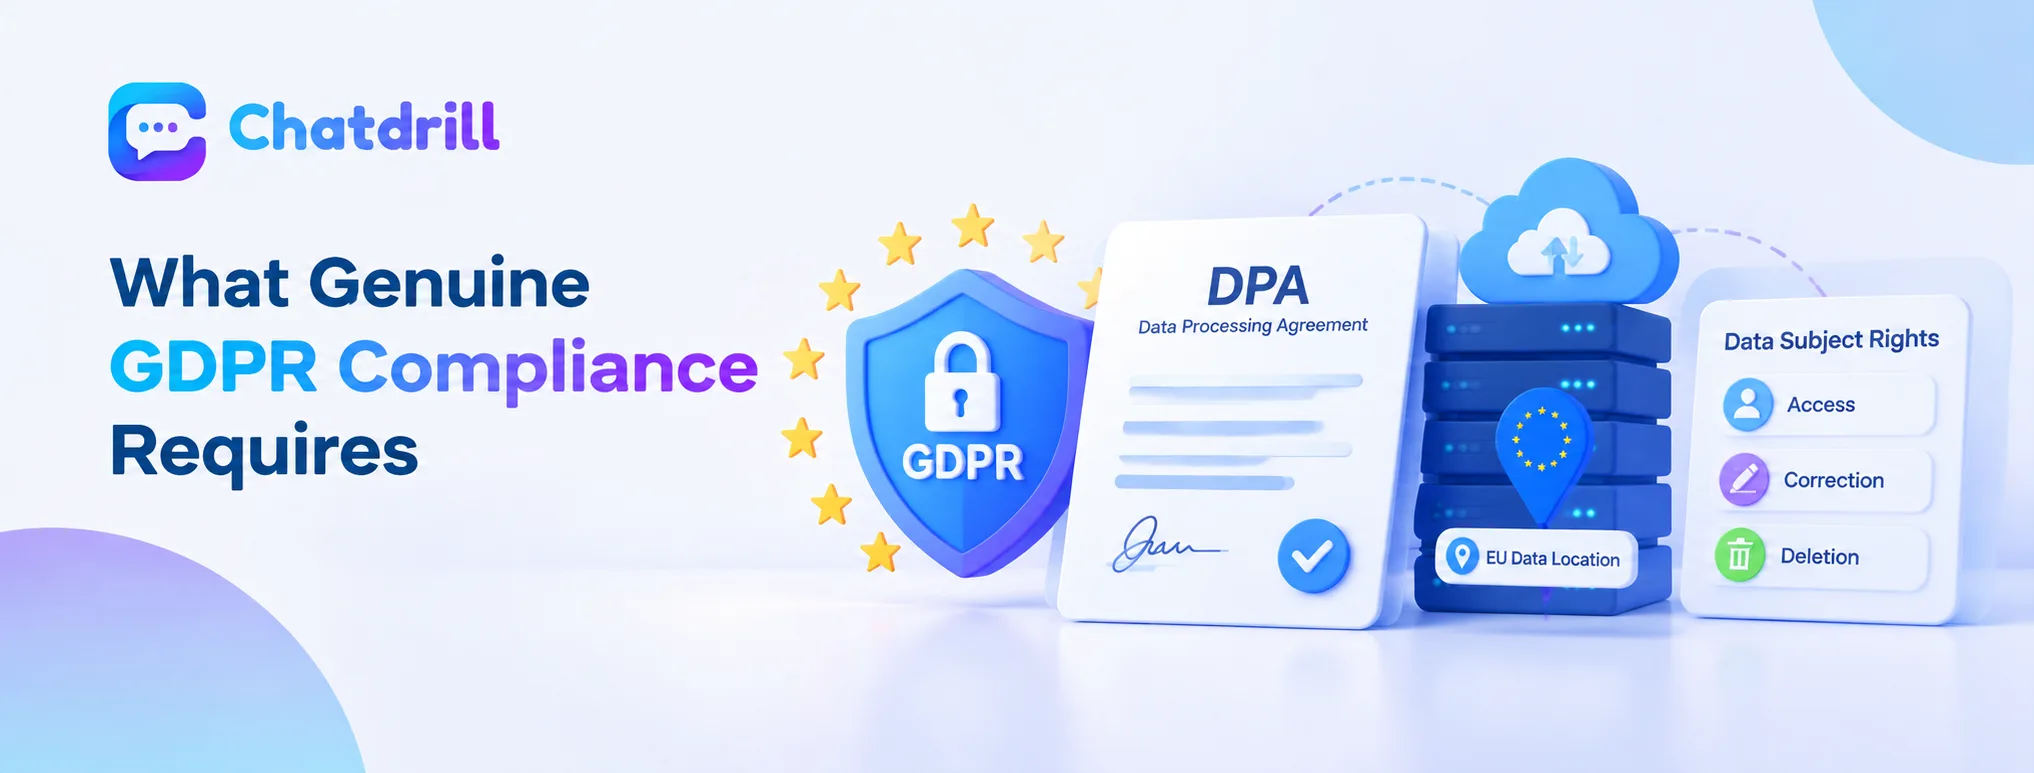
A signed Data Processing Agreement, verifiable data location, and genuine support for data subject rights together determine real compliance, beyond a general marketing claim.
A signed Data Processing Agreement and data location
A genuinely compliant vendor should offer a proper, signed Data Processing Agreement and disclose specifically where customer data is stored and processed, EU-based hosting being particularly relevant for many EU-facing businesses.
This specificity matters because a vague or unclear answer about data location or DPA terms often signals equally vague, unreliable compliance practices more broadly.
Genuine support for data subject rights
A genuinely compliant platform should support your ability to honor data subject rights, access, correction, and deletion requests, within GDPR's required timelines, not just claim general compliance in the abstract.
Confirming this specific operational capability, rather than assuming it from a general compliance badge, protects a business from a genuine, practical compliance gap.
Platforms Known for Strong Compliance Posture
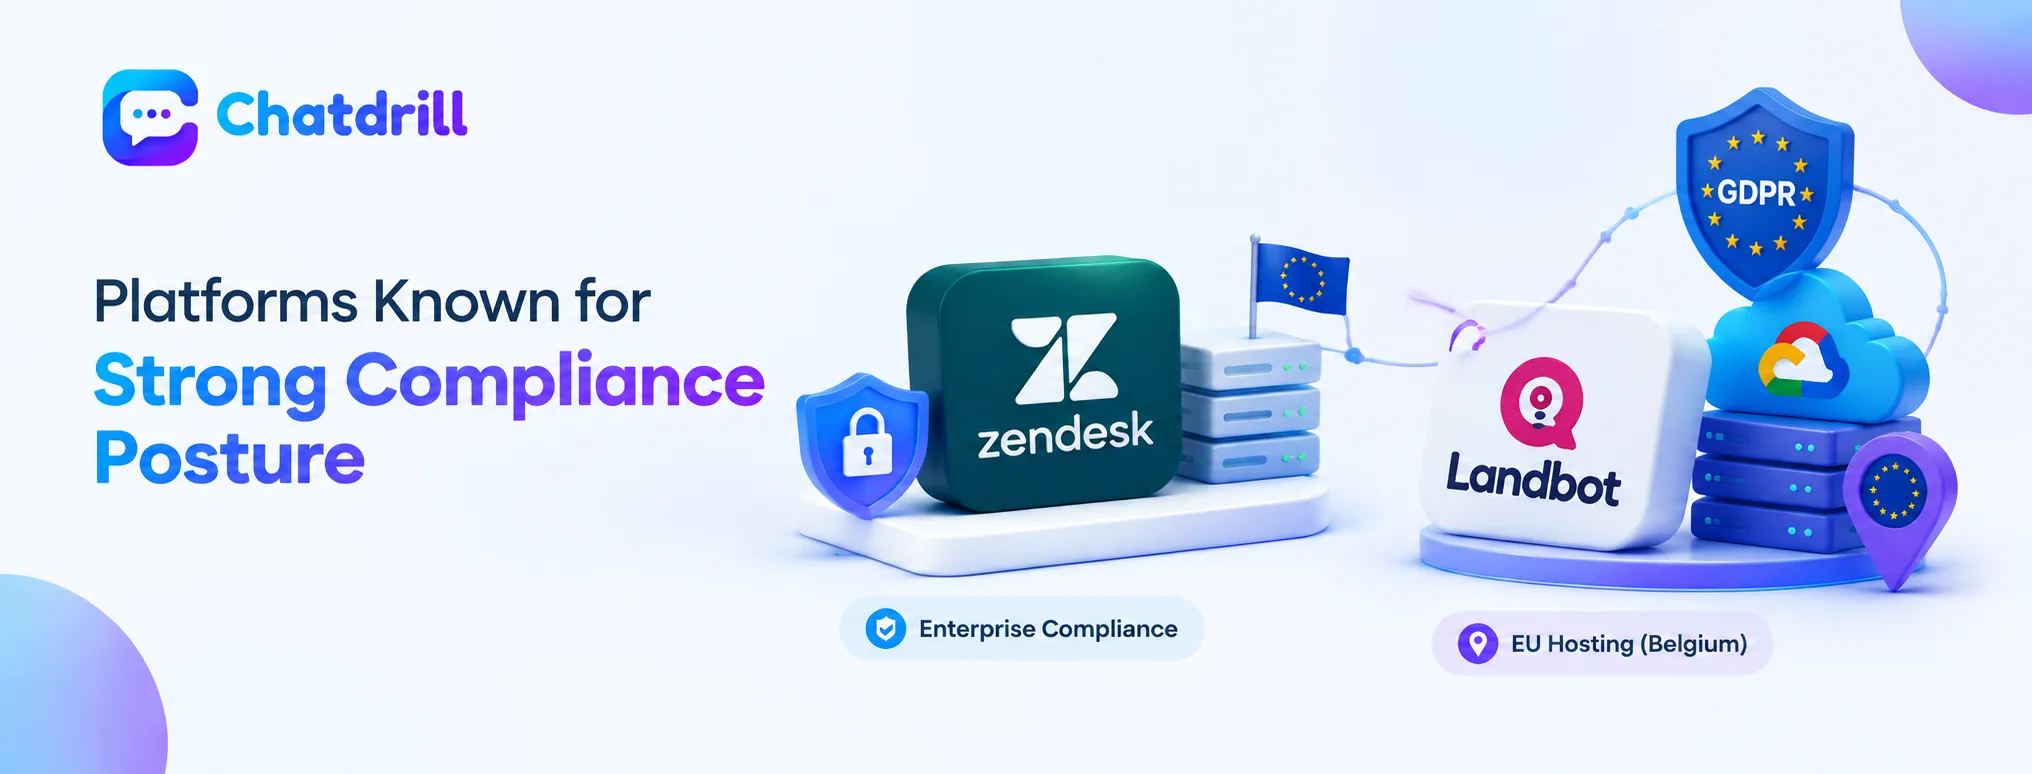
Zendesk and Landbot are commonly cited for specific, verifiable GDPR compliance infrastructure worth evaluating directly.
Zendesk for comprehensive enterprise compliance
Zendesk offers EU data residency and a comprehensive Data Processing Agreement across its suite, suiting a larger, established business needing GDPR compliance extended across a full customer service and chat workflow.
This comprehensive posture reflects Zendesk's broader enterprise positioning, with corresponding pricing to match this scope.
Landbot for EU-specific hosting
Landbot specifically hosts data in Belgium on Google Cloud Platform's EU infrastructure, a genuinely specific, verifiable data-residency detail worth noting for a business where EU data localization is a particular priority.
This kind of specific, named hosting location detail reflects exactly the verifiable specificity this guide recommends looking for, beyond a general compliance claim alone.
Common Mistakes in This Evaluation
Accepting a general compliance claim without verification, and overlooking whether AI training practices affect compliance, are common mistakes.
Accepting a general claim without verification
Treating any vendor's general "GDPR compliant" statement as sufficient, without directly verifying DPA terms, data location, and data subject rights support, risks discovering a genuine compliance gap only after committing to a platform.
Directly requesting and reviewing these specific details, as this guide recommends, produces a considerably more reliable evaluation than accepting a general marketing claim.
Overlooking AI training data practices
For an AI-assisted chat platform specifically, confirming whether customer conversation data is used to train shared AI models, and under what terms, represents a genuinely important, sometimes overlooked compliance dimension.
Asking this specific question directly, rather than assuming standard data handling applies to AI training as well, avoids this particular, modern compliance gap.
Key Questions to Ask Before Choosing
Requesting the actual DPA and asking specifically about data subject rights support are the most useful, concrete evaluation steps here.
Can I review your actual Data Processing Agreement?
Requesting the actual DPA document, rather than accepting a general assurance that one exists, lets you and your own legal counsel verify the specific terms genuinely apply to your situation.
A vendor genuinely prepared for GDPR compliance should readily provide this document without hesitation or excessive delay.
How do you support data subject access and deletion requests?
Asking specifically how the platform supports fulfilling a genuine data access or deletion request within GDPR's required timelines confirms operational, not just claimed, compliance capability.
This specific operational question matters more than a general compliance assurance, since it reveals whether the platform genuinely supports your practical, ongoing compliance obligations.